An independent firm dedicated to the cybersecurity of industrial environments
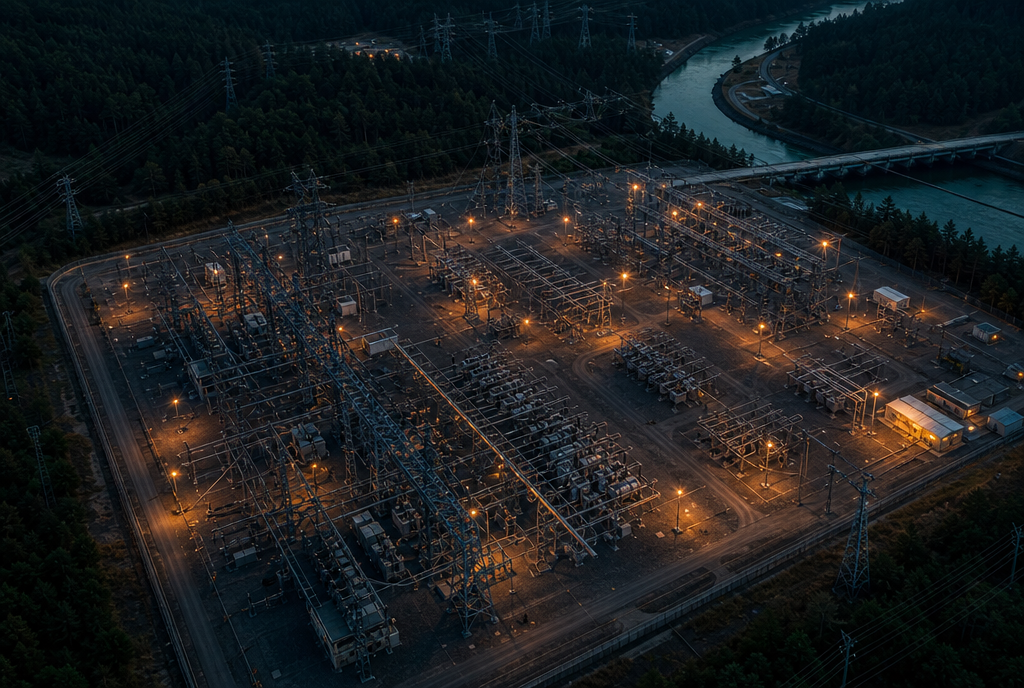
Leviotec is an independent firm specialized in OT (Operational Technology) cybersecurity. We secure the systems that run industrial facilities and critical infrastructure: power generation and distribution, industrial sites, transport. Our field of work is factories and substations, not office IT environments.
A career built at the heart of critical infrastructure
Before founding Leviotec, its founder spent 7 years at a major international engineering and energy group, leading cybersecurity audits and penetration tests on industrial facilities across Europe, Africa, and the Middle East

Within a major international group: 7 years of audits and penetration testing on industrial sites abroad
2025: Leviotec is founded to put this expertise directly at the service of industrial operators
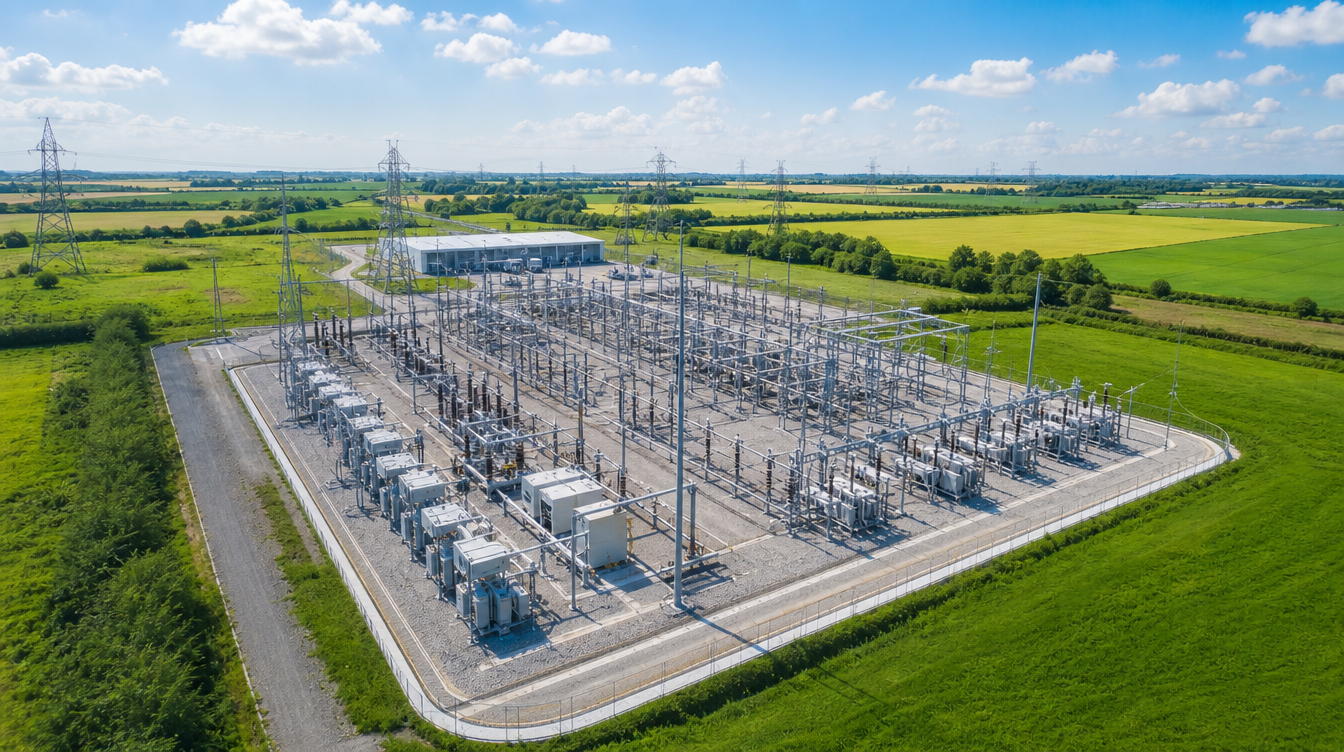
Today: engagements in France and internationally, from one-off audits to multi-year support
LEVIOTEC by the numbers
years of combined experience in industrial cybersecurity
audit and penetration testing missions completed
industrial sectors covered
[ our purpose ]
Protecting the systems that keep industry running.
We audit and test the PLCs, networks, and supervision systems that run industrial sites, without ever interrupting production. From substations to production lines, our work helps operators secure their OT environments with the same rigor as their IT systems.
Whether you operate a power grid, a production site, or drinking water infrastructure, we bring the technical depth and sector knowledge needed to turn an audit into a concrete action plan.
Founder & CEO
Daniel Rothman
Daniel brings 16 years of experience in industrial cybersecurity, gained on energy and manufacturing sites in France and internationally.

Founder & CEO
Dianne Walsh
Dianne leads IEC 62443 and NIS2 compliance audits, helping operators structure a realistic, well-documented path to compliance.
Our craft: OT cybersecurity
OT cybersecurity protects the systems that control physical equipment: programmable logic controllers, supervisory systems (SCADA), control networks. In these environments, an attack isn't measured in lost data: it results in a production shutdown, physical damage, or risk to people. That's what sets our craft apart from conventional IT cybersecurity.


[our process]
How we work
Audit, penetration testing, compliance, or training: we follow the same method, adapted to your operational constraints. Nothing is undertaken without you knowing what we'll do, when, and with what impact on production.

Methodological rigor
Our audits and penetration tests rely on industry frameworks, including IEC 62443, and on methodologies proven in production environments. Every intervention is scoped to never disrupt facility operations

Confidentiality
We work on sensitive infrastructure. Our deliverables, exchanges, and case studies are systematically anonymized: no confidential data, no identifiable site.

On-the-ground presence
Industrial cybersecurity cannot be audited remotely. We work on site in person, in France and internationally, alongside operations and maintenance teams

Long-term commitment
Industrial projects span several years. We support our clients throughout their programs, from the initial audit to ongoing security maintenance
"Leviotec mapped our industrial network without ever interrupting production. The report was clear to both our control engineers and management, with priorities we were able to act on as early as the following quarter."
"The IEC 62443 audit uncovered gaps we suspected but couldn't prove. The team knew how to talk to our control engineers without unnecessary jargon, and the remediation plan accounts for our production constraints."
"The training changed the way we respond in the field. Our technicians can now spot unusual behavior on the PLCs before it becomes an incident."
they trust us